Roles: who can do what
A role in Konzepti is granted inside a group, not on the account: one person is leader here, accountant there, and ordinary member in a third. And one member holds several roles in the same group.
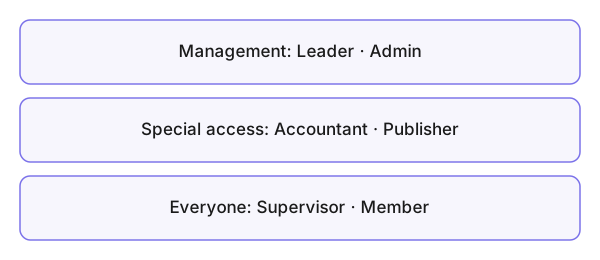
The table: who can do what
| Leader | Admin | Accountant | Publisher | Supervisor | Member | |
|---|---|---|---|---|---|---|
| Managing members and invitations | ✔ | ✔ | — | — | — | — |
| Group settings and deletion | ✔ | ✔ | — | — | — | — |
| The database and API keys | ✔ | ✔ | — | — | — | — |
| Accounting documents | ✔ | ✔ | ✔ | — | — | — |
| Publishing in the group's name | ✔ | ✔ | — | ✔ | — | — |
| Tasks, projects, messages, media | ✔ | ✔ | ✔ | ✔ | ✔ | ✔ |
Points to understand, not memorise
- The founder is protected: the group's creator is its leader; the role cannot be taken, nor the founder removed from their own group.
- Accountant is an access role, not a management role: they see the accounting archive, not the member administration.
- The role follows the sensitive data: the riskier something is (accounting, database, keys), the narrower its circle.